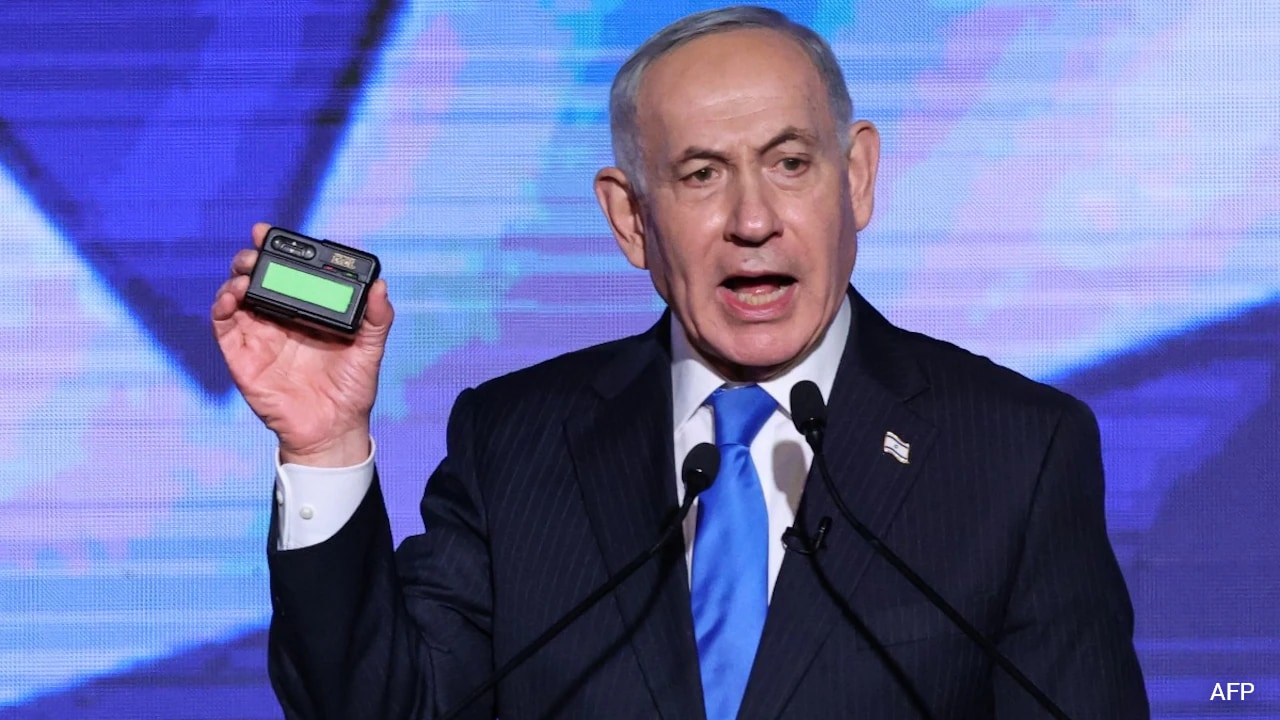
The headlines following the September 2024 pager detonations across Lebanon were uniform, lazy, and fundamentally wrong. Every major news outlet, defense analyst, and self-proclaimed intelligence guru rushed to label the operation as the ultimate cyber attack, a masterclass in remote hacking, or software manipulation taken to its horrific logical conclusion.
They are missing the entire point.
Calling the pager attack a cyber attack is like calling a sniper bullet a high-speed data transmission. It fundamentally misunderstands the physics, the supply chain reality, and the terrifyingly analog nature of modern statecraft. Nobody hacked a pager to make it explode. They built the bomb into the supply chain months before a single packet was ever routed.
If we keep misdiagnosing this event as a software vulnerability or a network breach, we are looking at the wrong threat entirely. We are preparing for a digital shield while our physical infrastructure is being packed with pentaerythritol tetranitrate at the factory floor.
The Software Myth and the Supply Chain Reality
Let us clear up the technical delusion immediately. A standard lithium-ion battery in a commercial pager or smartphone cannot be heated to thermal runaway simply by sending a malicious over-the-air command unless the hardware has been physically altered to accommodate that failure mode. Software can crash a processor, drain a battery, or lock a screen. Software cannot manufacture high explosives.
The consensus narrative loves the James Bond fantasy of a hacker sitting in a dark room, typing lines of code, and turning pocket-sized communication devices into grenades with a keystroke. It is clean. It sounds futuristic. It fits neatly into our modern obsession with invisible digital warfare.
It is also complete fiction.
Intelligence agencies did not exploit a zero-day vulnerability in the pager's operating system. They did something infinitely more pedestrian and infinitely harder to defend against. They intercepted the hardware manufacturing process. They established shell companies, manufactured modified circuit boards complete with secondary detonators and high-explosive compounds, and ensured these devices sailed right past procurement officers who thought they were securing reliable, low-tech communication gear to evade smartphone tracking.
This was not a failure of cybersecurity. This was a total collapse of physical supply chain integrity.
When you buy hardware from a source you cannot independently verify down to the individual silicon wafer and chemical composition of the solder, you do not have a network security problem. You have a Trojan horse sitting on your desk.
Why the Tech Industry Refuses to Face the Mirror
The tech sector and enterprise security consultants desperately want this to be classified as a cyber incident because it keeps the problem within their wheelhouse. If it is a cyber attack, you buy more endpoint protection, run more penetration tests, and hire more cybersecurity auditors. You sell more software.
If it is a physical supply chain interdiction of this scale, the traditional enterprise security playbook is useless. You cannot patch a block of PETN welded behind a battery pack with an over-the-air update.
I have watched companies spend millions of dollars on zero-trust network architectures while leaving their physical manufacturing outsourced to opaque third parties in regions with zero oversight. They audit code lines down to the semicolon while completely ignoring whether the factory assembling their IoT devices has a state-sponsored intelligence cell working the night shift.
The 2024 pager operation exposed a brutal blind spot in modern technology management: the complete decoupling of software trust from hardware provenance. We assume that because a device runs our code, the silicon it runs on is pure. We assume that because a communication tool is analog or low-tech, it is immune to advanced state-sponsored meddling.
History shows the exact opposite. The lower-tech the target, the easier it is to weaponize its physical construction without tripping digital tripwires.
The Strategic Aftermath Nobody Wants to Discuss
The international community spent weeks at the United Nations debating the ethics of remote warfare and the laws of armed conflict following the explosions. That debate, while necessary, completely sidestepped the practical panic gripping procurement departments worldwide.
Every intelligence agency, critical infrastructure operator, and multinational corporation just received a masterclass in what happens when your hardware supply chain is compromised years before deployment.
Consider the implications for industrial control systems, medical devices, automotive components, and grid infrastructure. If an actor can seed thousands of pagers with hidden explosives without detection, what stops them from doing the same to industrial switches, commercial vehicle ECUs, or backup generators?
Nothing. Nothing except the terrifying realization that modern globalized manufacturing is an open book to any intelligence service with sufficient capital and patience.
We are moving away from an era where security meant building higher digital walls. The Hezbollah pager operation proved that walls do not matter if you built the front gate yourself, unaware that the hinges were packed with explosives six months before delivery.
Stop looking for the zero-day exploit. Start looking at who built your hardware, where it was assembled, and what is hiding behind the battery pack.