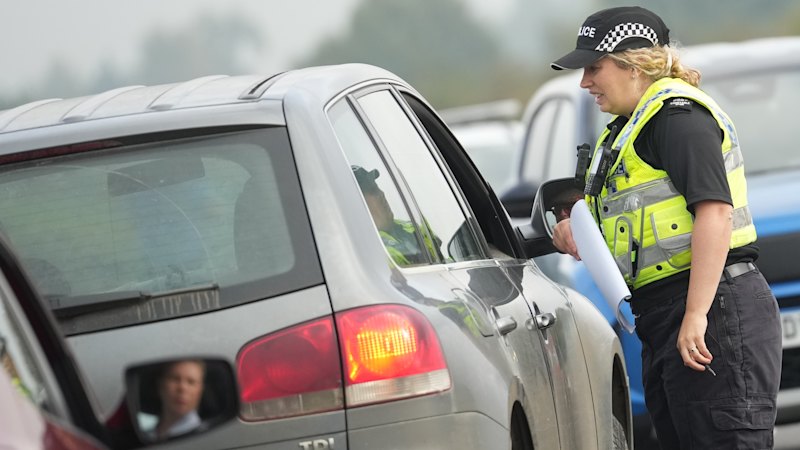
The operational integrity of critical military infrastructure relies on threat modeling that accounts for human friction, proxy networks, and early-stage self-preservation. When five individuals were detained near Royal Air Force Fairford in Gloucestershire following an alleged plot against the U.S.-operated bomber facility, the incident exposed a structural vulnerability not in perimeter security, but in the command-and-control reliability of decentralized proxy operatives. The primary operational anomaly of the event was singular: the incident did not unravel purely through traditional signal intelligence or automated surveillance arrays, but because one of the primary participants initiated a direct emergency call to law enforcement approximately an hour before local authorities were alerted by civilian observers.
Deconstructing this breakdown requires analyzing the mechanics of state-sponsored proxy networks, the cost function of low-level operational compliance, and the structural paradox of modern sabotage operations.
The Proxy Network Architecture and Principal-Agent Friction
In asymmetric security threats involving state-backed
The Structural Anatomy of Operational Failure Inside Critical Defense Infrastructure
news, technology
CATEGORY END
The security architecture guarding sensitive military installations operates under a fundamental assumption: external threat actors possess maximum intent while internal access controls serve as the primary defensive barrier. When this calculus fails, the point of rupture is rarely a sophisticated cyber intrusion or an elaborate paramilitary assault. It is an operational breakdown rooted in human error, psychological fragmentation, and systemic communication friction. The recent incident involving a foiled security breach at a United Kingdom air base, punctuated by a suspect inadvertently dialing emergency services, offers a stark clinical case study in the vulnerability of high-security perimeters to low-tier tactical execution.
To understand why a major security protocol nearly collapsed due to a civilian emergency call, one must examine the friction points between automated defensive response mechanisms and human-dependent verification loops. Security models applied to defense installations rely on tiered containment structures, yet these systems face specific systemic failure modes when stressors disrupt standard operating procedures.
The Three Vulnerability Vectors in Defense Perimeter Logic
Modern defense site security depends on the convergence of technical surveillance and human response discipline. When a breach occurs, or when an unauthorized entity attempts to establish a foothold, the defensive posture is typically compromised by three distinct failure vectors.
The first vector is input distortion during distress states. High-stress environments induce cognitive tunnel vision, degrading an operative or operative-adjacent individual's ability to maintain protocol compliance. In situations where actors experience abrupt shifts from planning to execution, cognitive overload often results in erratic actions. A suspect contacting emergency authorities directly represents an extreme manifestation of this distortion—an absolute decoupling of tactical intent from operational execution.
The second vector involves bureaucratic latency within multi-agency communication channels. When a civilian emergency dispatch center receives a call originating from or concerning a military installation, jurisdictional handoffs introduce critical time delays. Standard operating procedures dictate a verification hierarchy: local municipal dispatch must interface with base military police, who in turn must authenticate the threat level before deploying tactical assets. This friction creates a window of vulnerability where actionable intelligence sits trapped in administrative queues.
The third vector centers on asset deployment rigidity. Defense installations maintain fixed response quotas based on threat matrix projections. If an anomaly falls outside the parameters of anticipated threat vectors—such as an uncoordinated, legally chaotic individual stumbling through an operational zone—the response mechanism often exhibits false-positive filtering. Command structures hesitate to deploy heavy countermeasures until definitive hostile confirmation is achieved, leaving a brief window where physical access remains unchecked.
The Cost Function of Human Element Friction in Security Protocols
Quantifying the effectiveness of an installation's defense requires examining the cost function associated with human intervention. Automated sensors and biometric perimeters incur high capital expenditure but offer low variance in execution. Human operators and intruders, conversely, introduce high variance and unpredictable cost penalties.
When an intruder initiates contact with external authorities rather than completing an attack objective, the linear progression of the security incident halts. However, the cost function shifts abruptly from physical defense to information containment. The primary risk transforms from a kinetic breach to a compromise of operational security standards. The failure of the suspects involved in the UK air base incident highlights a broader principle: low-competence threat actors impose heavy administrative and investigative burdens on defense infrastructure, draining resources disproportionately relative to the actual kinetic threat posed.
This dynamic exposes a critical flaw in threat assessment modeling. Standard threat matrices calculate risk as a product of capability and intent. They frequently fail to account for incompetence as an independent variable. An actor lacking both capability and coherent intent introduces erratic noise into the security ecosystem, forcing defensive systems to react with maximum force to ambiguous indicators.
Systemic Corrections and Operational Hardening
Mitigating vulnerabilities exposed by erratic security breaches requires targeted adjustments to perimeter management and inter-agency response frameworks.
First, the integration of real-time communication intercept protocols must be tightened. Municipal emergency dispatch feeds adjacent to strategic military installations require automated keyword routing to military intelligence and base security operations centers. Eliminating the manual relay phase reduces communication latency from minutes to milliseconds, ensuring that self-reported anomalies trigger immediate tactical validation.
Second, security forces must implement adaptive response matrices that calibrate for behavioral anomaly rather than solely focusing on kinetic intrusion indicators. An individual exhibiting erratic behavioral patterns near a sensitive perimeter—regardless of whether they communicate with external entities—must be classified under an immediate containment protocol to prevent opportunistic exploitation of the site's response latency.
The incident at the UK air base demonstrates that the greatest threat to a fortified installation is not always the precision of an adversary, but the inherent unpredictability of human error within the operational chain. Strengthening these perimeters requires treating communication channels, internal verification speed, and psychological friction variables with the same rigor applied to physical barriers and electronic surveillance grids.
Deploy direct municipal-to-military communication bypass channels for all emergency dispatch nodes within a twenty-mile radius of strategic defense assets. This removes administrative handoff delays and collapses response validation loops to operational minimums.